AI Agent Governance: How Enterprises Manage Agent Ownership, Policies, and Lifecycle
Anil Nair is an enterprise AI strategist focused on AI governance, intelligent automation, agent orchestration, and the architecture required to deploy AI systems safely across complex organizations.
AI Agent Governance defines how enterprises establish accountability, ownership, policies, and lifecycle controls for AI agents. A governance framework ensures every agent has a documented purpose, responsible owners, approved responsibilities, review requirements, and escalation procedures. This enables enterprises to manage agent adoption while maintaining oversight, consistency, and accountability.
At AIQoD, governed agentic AI is approached through clear accountability, defined business responsibilities, and human oversight across enterprise operations. These principles help organizations establish governance foundations before expanding their use of AI agents.
What Is AI Agent Governance?
AI Agent Governance is the organizational framework used to define how AI agents are introduced, owned, approved, monitored, reviewed, and retired within an enterprise. It establishes accountability for agent purpose, responsibilities, operating policies, and business outcomes.
Unlike traditional software components, AI agents can interpret objectives and perform tasks across different business processes. This makes clear ownership and policy management necessary throughout the agent lifecycle.
Governance answers several important questions:
- Why does the agent exist?
- Which business process does it support?
- Who is responsible for the agent?
- Who approves its deployment and changes?
- How should its performance and behavior be reviewed?
- What happens when the agent is no longer required?
AI Agent Governance therefore connects business accountability, organizational policies, lifecycle management, and human oversight into one operating framework.
Why Enterprises Need AI Agent Governance
AI agent governance helps enterprises establish accountability, control operational risk, and ensure that AI agents operate within clearly defined business responsibilities. As organizations deploy more agents across departments, governance becomes necessary to manage ownership, approval requirements, policy compliance, and ongoing oversight.
Without a governance framework, organizations may struggle to identify who is responsible for an agent, why it was deployed, whether its purpose has changed, and when it should be reviewed or retired.
AI Agent Identity and Ownership
Every enterprise AI agent should have a clearly defined identity, purpose, and accountable owner. An agent registry helps organizations maintain a consistent record of the agents operating across business functions.
An enterprise agent registry should capture information such as:
- Agent name and business purpose
- Business owner and technical owner
- Department and workflow association
- Lifecycle status
- Risk and impact classification
- Approval date and next review date
Clear ownership ensures that agents are not treated as unmanaged software components. Business owners remain accountable for the agent's purpose and operational outcomes, while technical owners support its implementation and maintenance.
Microsoft's guidance on AI agent identity provides additional context on identity management, ownership, permissions, lifecycle considerations, and governance requirements for enterprise agents.
Governance Policies for Agent Responsibilities
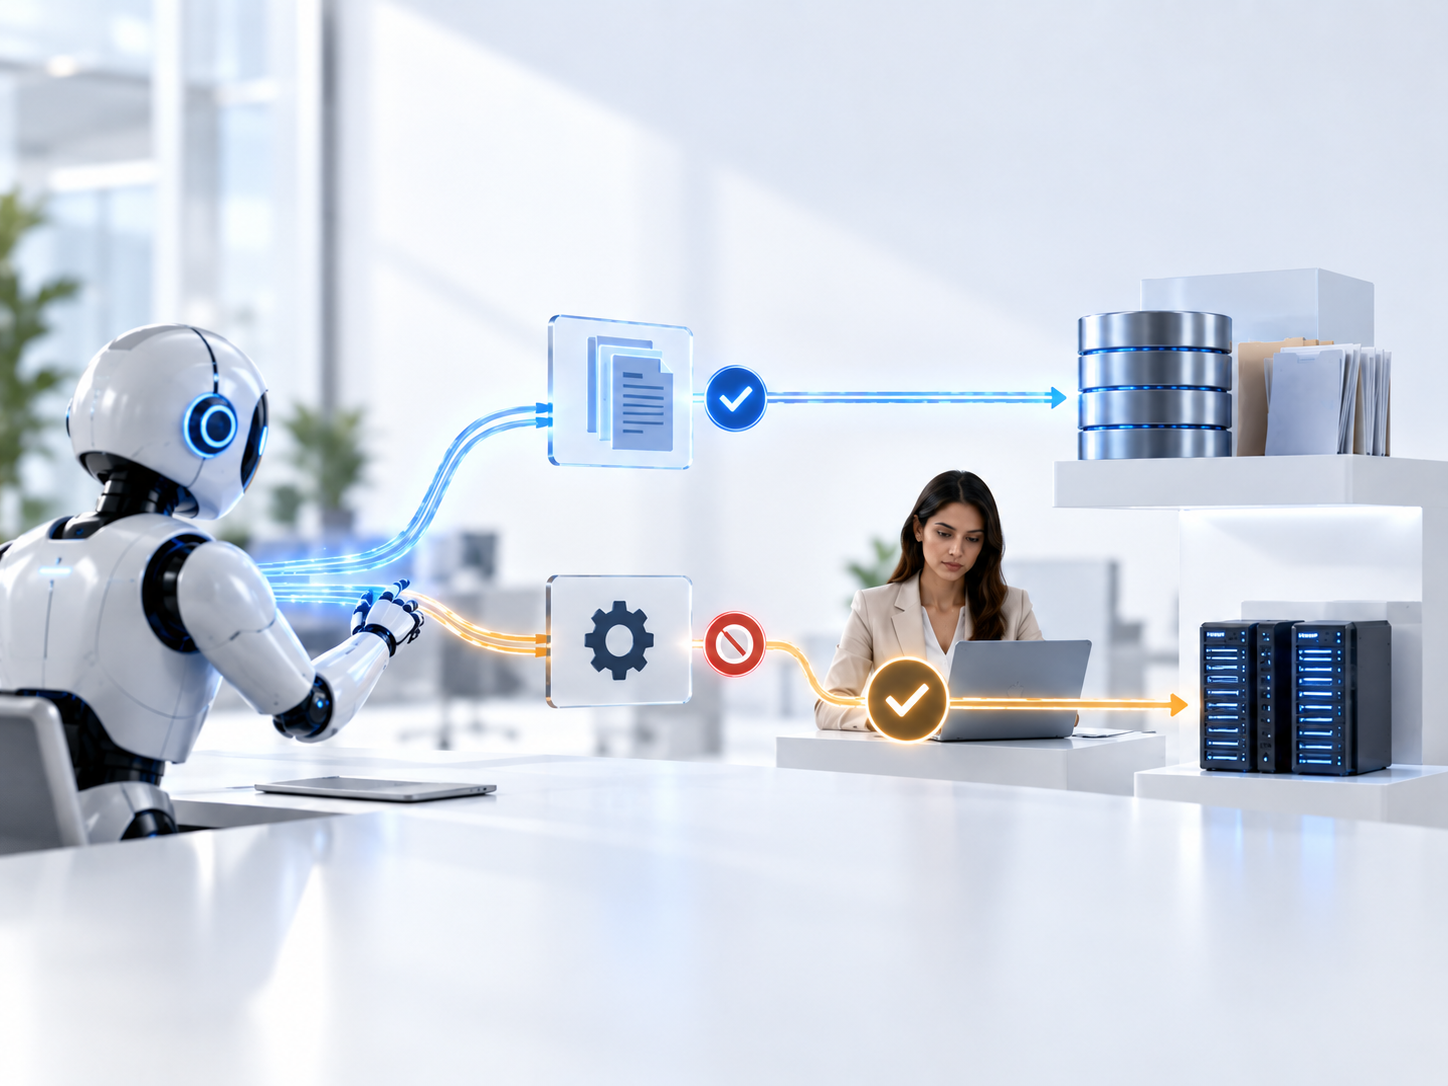
Governance policies define what an AI agent is responsible for and the business boundaries within which it can operate. These policies should connect each agent's capabilities to an approved business purpose.
For example, an agent responsible for invoice review may be authorized to identify discrepancies and prepare recommendations. Approving payments or changing vendor records may require separate responsibilities, approvals, and controls.
Effective governance policies should define:
- Approved business purpose
- Permitted responsibilities
- Prohibited activities
- Escalation requirements
- Review and approval conditions
Technical access controls and system permissions should be addressed separately within the organization's read and write security framework.
Governance of High Impact Responsibilities
Some AI agent responsibilities can create significant operational, financial, or compliance consequences. These responsibilities require stronger governance than routine information processing.
Enterprises should classify agent responsibilities according to their potential impact. A low impact activity may involve preparing an internal summary, while a high impact activity may influence payments, hiring decisions, regulatory reporting, or customer commitments.
High impact responsibilities should have:
- Clearly assigned ownership
- Documented approval requirements
- Defined escalation conditions
- Periodic policy reviews
- Evidence of decisions and actions
This approach allows governance requirements to reflect the consequences of an agent's responsibilities rather than applying identical controls to every use case.
Governance of Agent Responsibilities Across Systems
Enterprise AI agents often support workflows that involve multiple departments and business systems. Governance must therefore define the business responsibility of an agent across the complete workflow.
For example, an agent supporting procurement may interact with finance, vendor management, and approval teams. Each responsibility should have a defined owner, clear boundaries, and an escalation path when the agent encounters an exception.
Organizations should document:
- The business process supported by the agent
- The departments involved
- The responsibilities assigned to each agent
- The owner of the overall workflow
- The conditions requiring human intervention
Detailed system permissions, API access, and technical tool controls should be covered within the read and write security architecture.
Human Oversight in AI Agent Governance
Human oversight is a governance mechanism that defines when people must review, approve, or intervene in agent supported business processes. The requirement for human involvement should be established before deployment and documented as part of the agent's operating policy.
Not every responsibility requires the same level of oversight. Enterprises should classify responsibilities according to business impact, sensitivity, reversibility, and potential consequences.
- Routine Responsibilities: May operate within approved policies when the business owner has confirmed that additional approval is not required.
- Review Required Responsibilities: Involve important business decisions, external commitments, or changes to established processes, and may require review by an assigned employee or team.
- High Impact Responsibilities: Involve significant financial, regulatory, customer, or organizational consequences and should have clearly documented approval and escalation requirements.
Human oversight should be treated as an established governance requirement rather than an informal intervention used only after an issue occurs.
AI Agent Governance Requires Policy Ownership and Enforcement
Policies are effective only when an accountable owner is responsible for maintaining and enforcing them. Enterprises should establish clear ownership for governance standards, approval processes, exceptions, and policy updates.
Policy ownership should cover the complete agent lifecycle, including initial approval, operational reviews, changes in responsibility, and retirement. When an agent's business purpose or operating environment changes, its governance requirements should be reassessed.
A practical governance model should establish:
- Who creates and approves policies
- Who reviews exceptions
- Who authorizes changes in responsibility
- Who investigates policy violations
- Who can suspend or retire an agent
This creates a clear connection between governance decisions and organizational accountability.
Governance Monitoring and Auditability
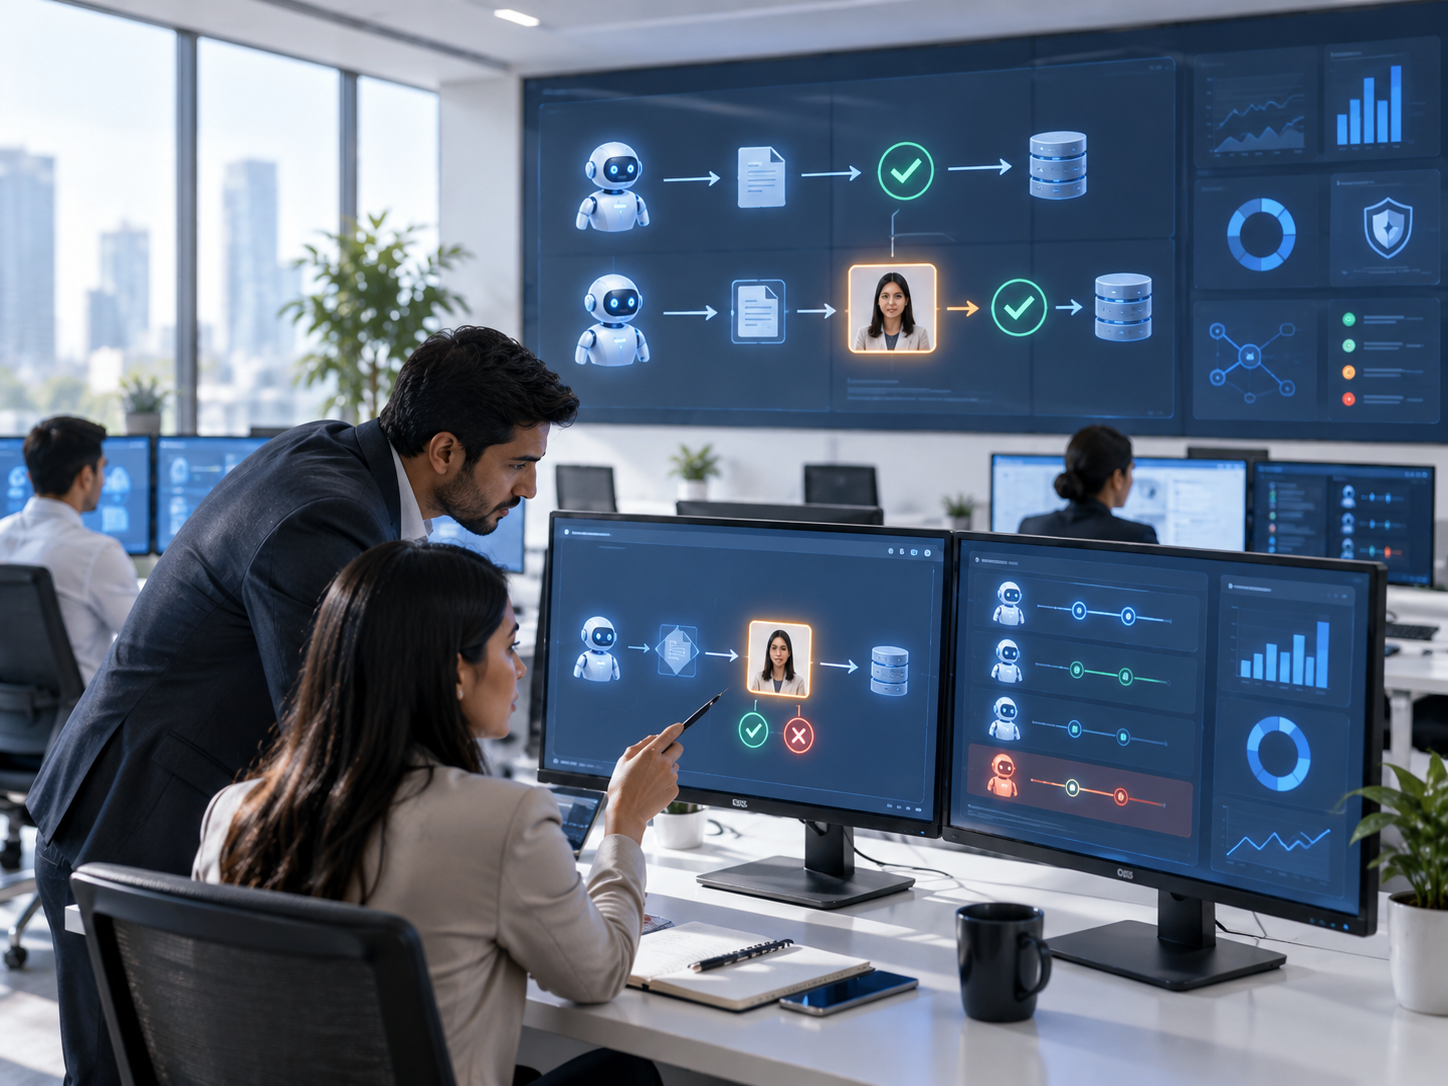
Governance monitoring helps enterprises verify that AI agents continue to operate according to their approved purpose, ownership, and policies. Auditability provides evidence of important governance decisions, changes, exceptions, and reviews.
Monitoring should not focus only on technical performance. It should also examine whether an agent's responsibilities, owner, risk classification, and business purpose remain accurate.
Important governance records include:
- Ownership changes
- Policy updates
- Approval decisions
- Exceptions and escalations
- Review outcomes
- Suspension or retirement decisions
Regular monitoring enables organizations to identify agents that require reassessment, additional oversight, or retirement.
Within AIQoD's approach to governed autonomous operations, visibility into agent ownership, policy decisions, workflow responsibilities, and escalation requirements supports ongoing governance reviews. This helps enterprises assess whether agents continue to operate within their approved business purpose and governance boundaries.
AWS guidance on governing agentic AI provides additional considerations for enterprise governance, including agent responsibilities, oversight, auditability, and operational controls.
Governance Across Multi Agent Workflows
Multi agent workflows require governance at both the individual agent level and the overall workflow level. Each agent should have a defined responsibility, while the complete workflow should have an accountable owner.
For example, a recruitment workflow may involve separate agents for job description analysis, candidate screening, interview scheduling, and reporting. Governance should clarify the responsibility of each agent and identify who owns the overall recruitment process.
A governance framework should define:
- The owner of the complete workflow
- The responsibilities of individual agents
- Escalation points between workflow stages
- Review requirements for material changes
- Accountability for the final business outcome
Detailed agent routing, delegation, communication, and context transfer should be addressed in the dedicated AI agent orchestration article.
Agent Ownership and Lifecycle Governance
An AI agent should have a defined lifecycle from initial proposal to retirement. Governance ensures that an agent is not introduced, changed, or retained without an accountable owner and an approved business purpose.
A practical governance lifecycle contains six stages:
- Propose: Document the business problem, expected value, intended users, and proposed responsibilities.
- Register: Record the agent's identity, business owner, technical owner, department, purpose, and lifecycle status.
- Review and Approve: Evaluate the agent's business purpose, risk classification, oversight requirements, and expected impact before deployment.
- Operate: Monitor whether the agent continues to meet its approved purpose and governance requirements.
- Review and Change: Reassess the agent when its purpose, owner, responsibilities, business process, or operating conditions change.
- Suspend or Retire: Suspend or retire the agent when it no longer meets business requirements, creates unacceptable risk, or is no longer needed.
Lifecycle governance prevents abandoned agents from remaining active without ownership or review. It also creates a documented process for handling changes throughout the agent's operational life.
How to Implement AI Agent Governance
AI Agent Governance works best when implemented as an operational framework supported by clear ownership, documented policies, and recurring reviews.
Step 1: Create an Agent Registry
Create a central inventory of all proposed, active, suspended, and retired agents. Record the agent's purpose, business owner, technical owner, department, lifecycle status, risk classification, and review date.
Step 2: Assign Clear Ownership
Assign a responsible business owner for every agent. Where required, assign a separate technical owner responsible for implementation, maintenance, and operational support.
Step 3: Document the Agent's Purpose
Define the business problem the agent is intended to address. Document its approved responsibilities, intended users, expected outcomes, and boundaries of responsibility.
Step 4: Classify Business Impact
Classify the agent according to the potential impact of its responsibilities. Use the classification to establish appropriate approval, oversight, escalation, and review requirements.
Step 5: Establish Governance Policies
Define the policies that apply to the agent, including ownership, acceptable use, human oversight, exception handling, review frequency, and change approval.
Step 6: Establish Approval and Escalation Procedures
Document which decisions require human review and identify the people or teams responsible for approval. Escalation procedures should be established before the agent is deployed.
Step 7: Monitor Governance Compliance
Review agent ownership, lifecycle status, policy compliance, exceptions, and changes to approved responsibilities. Use documented review outcomes to determine whether the agent should continue operating.
Step 8: Review, Suspend, or Retire
Review agents at defined intervals and whenever their purpose or operating conditions change. Suspend or retire agents that no longer have a valid business purpose or do not meet governance requirements.
Common AI Agent Governance Mistakes
The most common governance failures occur when enterprises deploy agents without treating ownership, approval, and lifecycle management as ongoing responsibilities.
- Deploying Agents Without a Registry: When agents are not recorded in a central inventory, enterprises may lose visibility into their purpose, ownership, and lifecycle status.
- Failing to Assign an Owner: An agent without a clearly assigned business owner creates uncertainty about accountability, policy approval, and ongoing review.
- Approving an Agent Only Once: Governance should continue after deployment. Changes to business purpose, responsibilities, ownership, or operating conditions should trigger an appropriate review.
- Leaving the Business Purpose Undefined: Every agent should have a documented purpose that explains why it exists and which business process it supports.
- Ignoring Exceptions and Escalations: Agents should have documented procedures for handling unexpected outcomes, policy exceptions, and situations requiring human judgment.
- Failing to Retire Unnecessary Agents: Agents that are no longer required should be formally suspended or retired through an approved lifecycle process.
- Separating Governance From Business Ownership: Governance is more effective when business owners participate in approval, monitoring, review, and retirement decisions rather than leaving all responsibility to technical teams.
AI Agent Governance Within the Enterprise Intelligence Layer
The Enterprise Intelligence Layer provides the broader environment in which enterprise agents can access shared context, coordinate business processes, and support operational workflows. AI Agent Governance defines the organizational policies and accountability requirements that apply to those agents.
The two concepts serve different purposes.
The Enterprise Intelligence Layer supports enterprise context, coordination, and operational visibility. AI Agent Governance establishes agent ownership, approved responsibilities, lifecycle management, oversight, and accountability.
Detailed architecture and orchestration responsibilities should be covered in the related Enterprise Intelligence Layer and AI Agent Orchestration articles.
The central governance principle is simple: an agent may support a business objective, but its continued operation must remain connected to a documented purpose, accountable ownership, and approved governance requirements.
Conclusion
AI Agent Governance provides enterprises with a structured approach to managing agent ownership, policies, oversight, and lifecycle responsibilities.
A strong governance framework gives every agent a documented purpose, accountable owners, defined approval requirements, review procedures, and clear conditions for suspension or retirement.
Governance should continue throughout the agent lifecycle rather than ending at deployment. Regular reviews help enterprises ensure that agents remain aligned with business objectives and approved operating requirements.
The objective is to support responsible agent adoption through clear accountability, consistent policies, and measurable oversight.
Frequently Asked Questions
What is AI Agent Governance?
AI Agent Governance is the framework used to manage the ownership, purpose, approval, oversight, and lifecycle of enterprise AI agents. It ensures that agents remain accountable and aligned with approved business requirements.
Who should own an enterprise AI agent?
Every agent should have a responsible business owner who is accountable for its purpose, business outcomes, and continued use. A separate technical owner may manage implementation, maintenance, and operational support.
What should an enterprise agent registry contain?
An agent registry should record the agent's identity, business purpose, owners, department, lifecycle status, risk classification, approved responsibilities, and review information. It provides a central source of governance visibility.
How often should enterprises review AI agents?
Agents should be reviewed at defined intervals and whenever their purpose, ownership, responsibilities, or operating conditions change. The review frequency should reflect the agent's business impact and governance requirements.