Read and Write Security for AI Agents: Controlling Enterprise Actions
Anil Nair is an enterprise AI strategist focused on AI governance, intelligent automation, agent orchestration, and the architecture required to deploy AI systems safely across complex organizations.
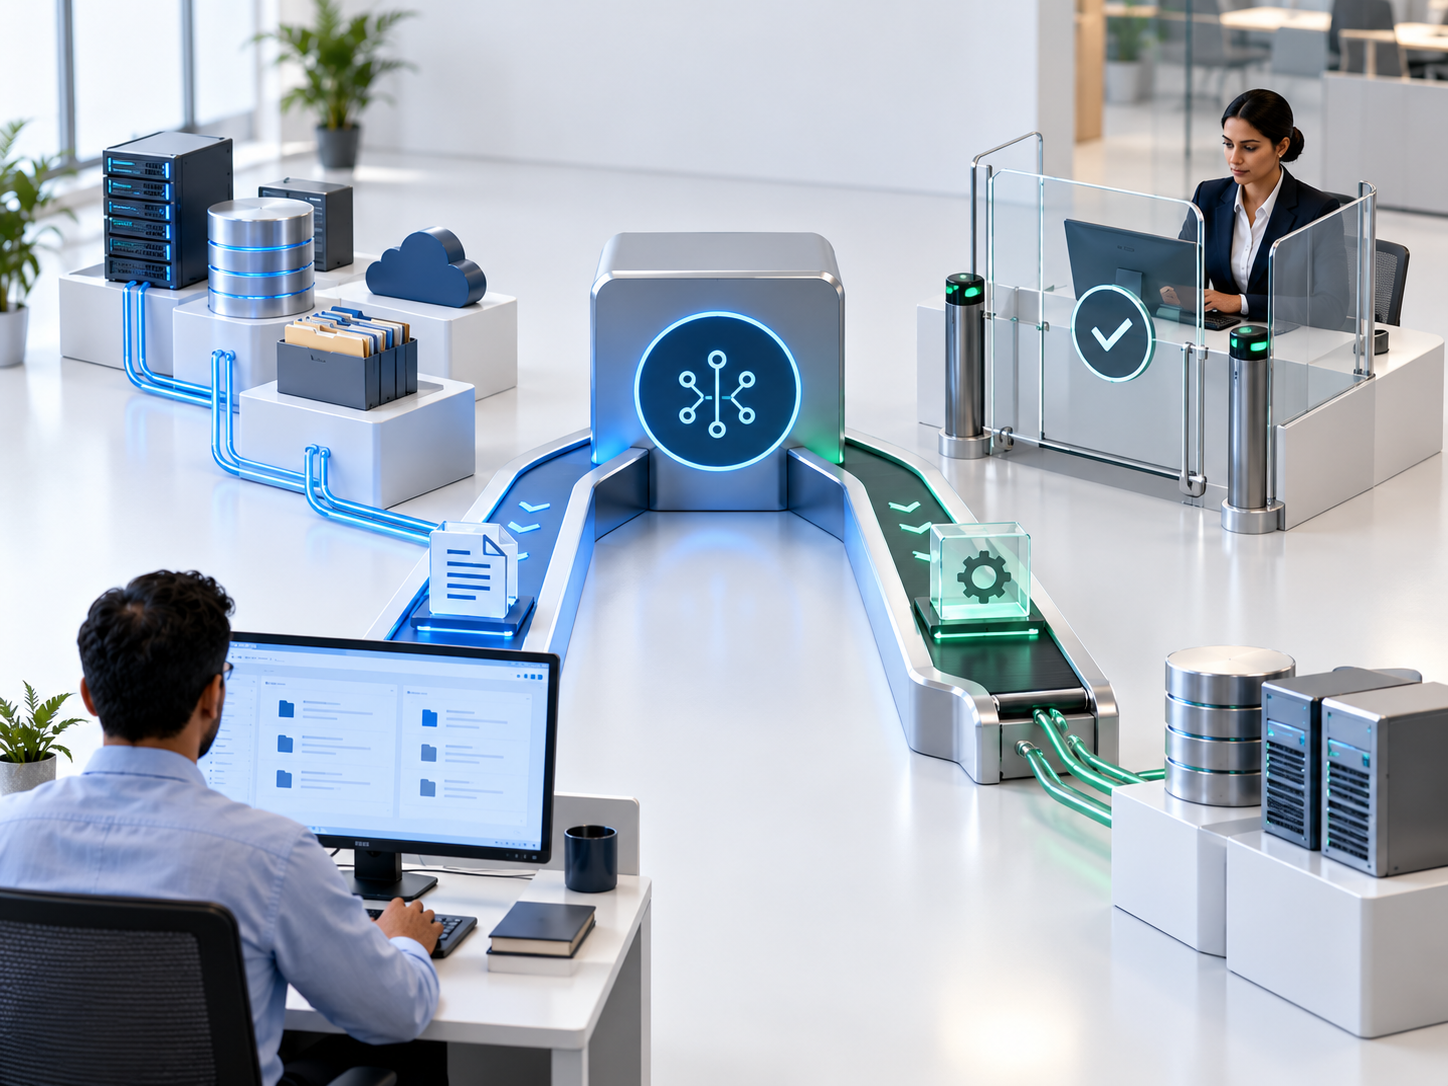
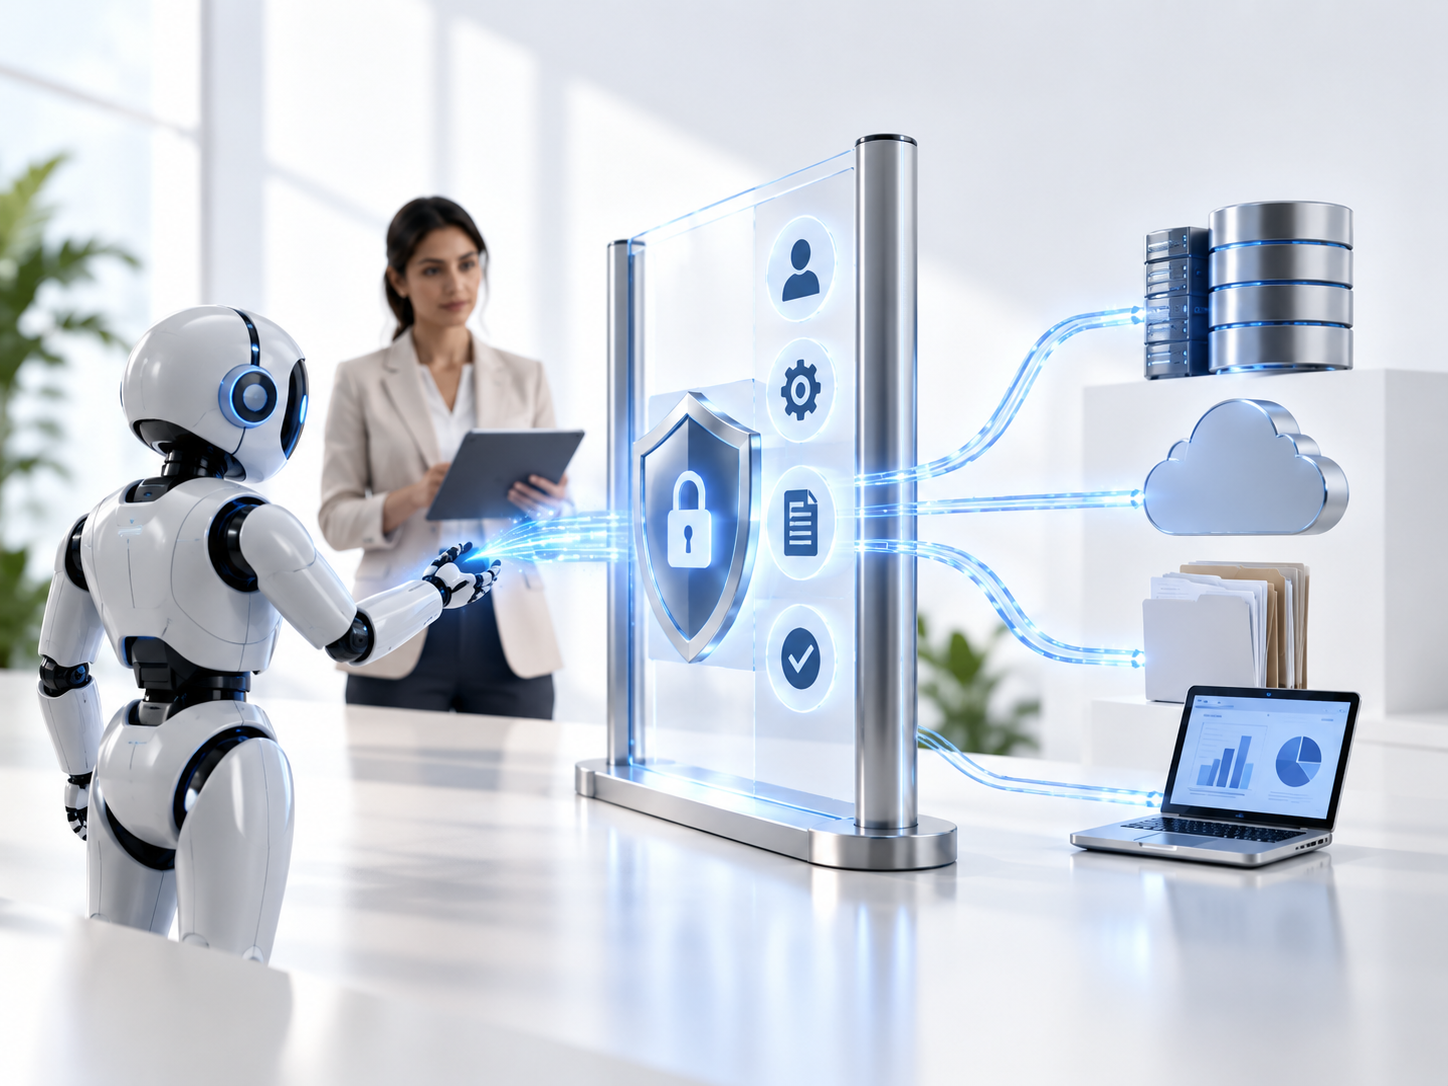
Read and Write Security for AI Agents defines how enterprises control the information agents can retrieve and the changes they can make across business systems. Effective security separates read permissions from write permissions, limits tool access, enforces approval gates, protects credentials and records every important action for accountability.
What Is Read and Write Security for AI Agents?
Read and Write Security for AI Agents is an access control approach that distinguishes information retrieval from actions that change enterprise data or system state. It ensures an agent receives only the permissions required for its assigned task.
An agent may need to read customer records, inspect an invoice, or retrieve employee information. However, reading that information does not automatically justify updating records, issuing payments, deleting data or changing system configurations.
The central principle is straightforward: permission to understand information should not automatically grant permission to change it.
This separation becomes important when AI agents interact with enterprise applications, databases, APIs, financial systems and operational tools.
Why Enterprises Need Separate Read and Write Controls
Read and write permissions create different levels of operational exposure. Read access allows an agent to retrieve information, while write access can change business records, trigger transactions or create consequences outside the original workflow.
An enterprise customer service agent, for example, may be permitted to retrieve order details and prepare a response. It may require additional authorization before modifying an order, issuing a refund or changing delivery information.
Without separate controls, an agent with broad system access may be able to perform actions beyond its intended purpose.
Common risks include:
- Unrestricted modification of enterprise records
- Unauthorized financial or operational transactions
- Accidental deletion or overwriting of information
- Excessive permissions inherited from connected tools
- Changes made without human review
- Difficulty identifying which agent performed an action
- Insufficient controls around sensitive data
Read and write security therefore needs to be implemented at the system and tool boundaries, rather than relying only on instructions inside an agent prompt.
Read Access and Write Access Are Different Security Boundaries
Read access allows an agent to obtain information. Write access allows the agent to create, modify, delete or otherwise change information or system state.
These permissions should be evaluated separately, even when both are available through the same application or API.
| Permission | Typical Activity | Security Consideration |
|---|---|---|
| Read | Retrieve customer records | Limit accessible records and fields |
| Search | Find relevant documents | Restrict search scope and sensitive results |
| Prepare | Draft an update or transaction | Prevent execution before authorization |
| Write | Modify an existing record | Validate the requested change |
| Create | Generate a new record or request | Check required fields and business rules |
| Delete | Remove information | Apply stronger authorization and recovery controls |
| Execute | Trigger a transaction or external action | Require appropriate policy checks and approval |
A system may expose all these capabilities through one API. The security architecture should still distinguish the specific operations an agent is authorized to perform.
Least Privilege for AI Agent Read and Write Access
Least privilege means giving an agent only the permissions necessary for its defined responsibilities. For AI agents, this principle should apply to data, systems, tools, fields, operations and transaction values.
A procurement agent may need to read supplier details and prepare purchase requests. It may not need permission to modify supplier banking information or approve unrestricted payments.
A practical access model considers five dimensions:
- System scope: Which applications can the agent access?
- Data scope: Which records and data categories can it retrieve?
- Field scope: Which individual fields are visible or editable?
- Operation scope: Which actions can it perform?
- Transaction scope: What limits apply to financial or operational changes?
The same agent might be allowed to read an invoice amount but not change the amount. It might prepare a payment request but require a separate approval before execution.
This approach reduces the consequences of incorrect decisions, compromised credentials, and unintended instructions.
Control Read Access at the Data and Field Level
Read security should not stop at application level permissions. Enterprises may also need to control which records, fields and data categories an agent can retrieve.
An HR agent, for example, might access employee department information while being restricted from retrieving sensitive personal details. A finance agent might access invoice metadata but not unrestricted employee banking information.
- Record Level Access: Determines which specific business records an agent can retrieve. A support agent may only access cases assigned to its authorized region or service function.
- Field Level Access: Determines which fields within a record are visible. An agent may see an invoice number and payment status while sensitive bank account details remain unavailable.
- Context Based Access: Evaluates the reason for the request, the initiating user, the workflow and the agent's approved purpose. Access can be restricted when the request falls outside the expected business context.
- Data Classification: Identifies sensitive information that requires stronger controls. Financial, personal, regulatory and confidential business information may need separate access policies.
These controls help prevent an agent from retrieving more information than is necessary to complete the assigned task.
Write Security Requires Explicit Action Authorization
Write security controls whether an agent can change enterprise data or initiate an operational action. Authorization should evaluate the requested operation rather than assuming that access to a system grants unrestricted authority.
For example, an accounts payable agent may be allowed to create a draft invoice record. It may not be allowed to approve payment, change supplier banking details or release funds.
A write authorization process can evaluate:
- Agent identity
- Requesting user or workflow
- Target system
- Target record
- Requested operation
- Data being changed
- Transaction amount
- Business rules
- Approval requirements
- Audit requirements
The authorization decision should occur before the write operation is executed.
Prepare and execute are separate activities. An agent can prepare a proposed change without automatically receiving permission to apply that change.
Use Approval Gates Before High Impact Writes
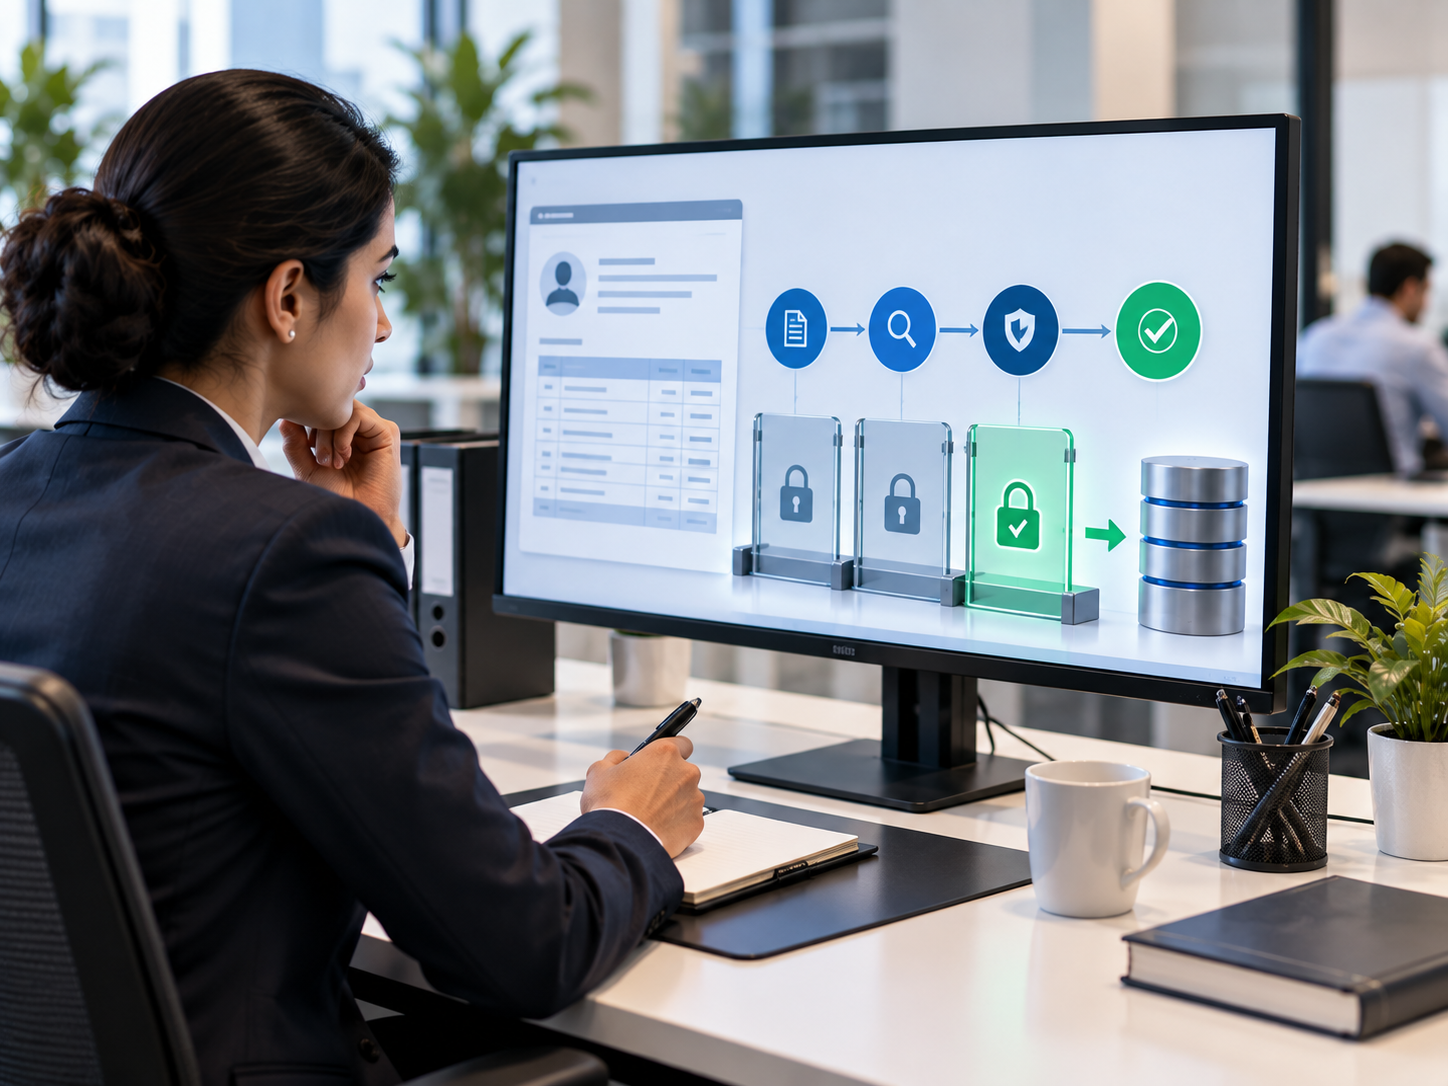
Human approval creates a control point before sensitive actions are executed. The approval requirement should be based on the risk and impact of the operation.
For example, an agent may be permitted to update a low risk workflow status automatically. A payment release, access permission change or deletion of critical information may require explicit approval.
Low Impact Writes
Low impact writes may be permitted when the operation is reversible, clearly defined and within approved limits. Examples include updating a task status, adding a classification tag, recording a workflow timestamp, and saving a draft response.
Moderate Impact Writes
Moderate impact writes may require additional validation or conditional approval. Examples include changing operational priorities, updating customer contact information, creating a service request, and sending an external business communication.
High Impact Writes
High impact writes should normally require stronger authorization and where appropriate, human approval. Examples include releasing a financial payment, changing access permissions, deleting important records, modifying sensitive employee information, changing supplier banking details, and executing an irreversible transaction.
A practical controlled workflow is: Read → Analyze → Prepare → Validate → Approve → Write → Audit.
Not every workflow needs every stage, but the architecture should explicitly define where authorization and approval are required.
Secure the Tools and APIs Used by AI Agents
Tools and APIs provide agents with the ability to interact with enterprise systems. Read and write security must therefore be implemented through the operations exposed by those tools.
An API that offers both retrieval and modification functions should not be treated as a single unrestricted capability.
For each tool, enterprises should define:
- Permitted agents
- Permitted operations
- Accessible data scope
- Allowed parameters
- Transaction limits
- Approval conditions
- Logging requirements
- Credential requirements
- Failure handling behavior
Consider an order management API. An agent may be allowed to retrieve order status, but a separate permission may be required to cancel an order or issue a refund.
Tool access should be evaluated according to the exact operation being requested.
Zero trust architecture provides a useful security model for AI agent access because it requires access requests to be evaluated rather than automatically trusted based on network location or previous access. NIST's zero trust guidance explains the importance of protecting resources through explicit authentication and authorization, which supports operation specific access controls for enterprise agents.
Protect Credentials and Agent Access Tokens
Credentials determine how an agent authenticates to enterprise systems. Poor credential management can undermine otherwise effective access policies.
Agents should use controlled identities and credentials that are appropriate for their authorized tasks. Shared human credentials make it difficult to distinguish automated activity from individual user activity.
Important credential controls include:
- Use dedicated agent identities where appropriate
- Store secrets in approved credential management systems
- Avoid embedding credentials in prompts or source code
- Limit token permissions and validity
- Rotate credentials according to organizational policy
- Revoke access when an agent is retired or compromised
- Record the identity associated with important operations
Credential possession should not be treated as unrestricted operational authority. The system should still evaluate whether the requested action is permitted.
Prevent Excessive Agency in Write Operations
Excessive agency occurs when an agent has more authority, tool access or operational freedom than its task requires. The risk increases when an agent can independently perform consequential actions across several connected systems.
For example, a finance agent might be designed to identify duplicate invoices. It does not necessarily need permission to modify supplier records, release payments and change accounting configurations.
The OWASP GenAI Security Project identifies excessive agency as an important security consideration for applications that use AI agents. Its guidance highlights the need to limit agent functionality, permissions, and autonomy so that an agent cannot perform unnecessary or unauthorized actions through connected tools.
Security design should limit the agent to the smallest set of capabilities required for the workflow. A useful separation is:
| Agent Responsibility | Appropriate Capability |
|---|---|
| Identify a potential duplicate | Read invoice and supplier data |
| Prepare a review case | Create a draft case |
| Recommend an action | Generate a proposed decision |
| Approve a payment | Separate authorization approval |
| Release a payment | Restricted execution capability |
This model reduces the chance that a single incorrect decision can trigger multiple high impact actions.
Apply Transaction Limits and Business Rules
Transaction limits restrict the value, frequency, destination, or type of action an agent can perform. These limits are particularly relevant to financial, procurement, customer service and operational workflows.
A payment agent, for example, might be allowed to prepare payment requests below a defined value while requiring additional authorization for larger amounts. The specific thresholds should be established by the enterprise's policies and risk assessments.
Business rules may evaluate:
- Transaction value
- Currency
- Supplier status
- Customer status
- Duplicate transaction indicators
- Approval history
- Time of request
- Destination account
- Frequency of actions
Transaction limits should be enforced by the system processing the request. They should not depend only on an agent's internal instructions.
Implement Read and Write Auditability
Auditability creates a record of important agent access and action events. It helps enterprises understand what information was accessed, which operation was requested, which controls were applied and what result occurred.
A useful audit record may include:
- Agent identity
- User or workflow context
- Timestamp
- Target system
- Target record
- Requested operation
- Data scope
- Authorization decision
- Approval status
- Execution result
- Exception details
- Correlation identifier
The audit record should distinguish between a proposed action and an executed action.
For example, the system should be able to identify whether an agent only prepared a payment request or actually released the payment.
Audit records should also be protected against unauthorized alteration and retained according to applicable organizational and regulatory requirements.
Design Failure Handling and Rollback for Writes
Write operations can fail because of invalid data, permission errors, system outages, conflicting updates or interrupted workflows. Security architecture should define what happens when an action is partially completed or produces an unexpected result.
Important safeguards include:
- Validation Before Execution: Validate data and business rules before committing a change. This reduces errors caused by incomplete or inconsistent inputs.
- Idempotent Operations: Where possible, design operations so that repeated requests do not unintentionally create duplicate changes or transactions.
- Transaction Boundaries: Define which operations should succeed together and which should be handled separately. This helps reduce inconsistent system state.
- Rollback and Recovery: Where technically possible, provide a method to reverse or recover from an incorrect change. Not every action can be reversed, so irreversible operations require stronger controls before execution.
- Exception Escalation: Escalate uncertain, failed or high impact operations to an appropriate human or controlled workflow.
A reliable system should not assume that every write operation will succeed simply because an agent requested it.
How to Implement Read and Write Security for AI Agents
Read and write security should be introduced through a structured implementation process that connects agent responsibilities with technical enforcement.
Step 1: Map Agent Activities
Document every system, data category, tool and operation the agent may need. Separate information retrieval from actions that change enterprise state.
Step 2: Classify Operations
Group operations into read, prepare, create, update, delete and execute categories. Identify which operations have financial, regulatory, customer or operational consequences.
Step 3: Define Minimum Permissions
Assign only the permissions necessary for each task. Restrict access by system, record, field, operation and transaction value where appropriate.
Step 4: Create Authorization Rules
Define the conditions under which the agent can perform each operation. Evaluate identity, context, requested action, data scope and applicable business rules.
Step 5: Add Approval Gates
Identify actions that require human approval or stronger authorization. Ensure approval occurs before the sensitive operation is executed.
Step 6: Enforce Controls at the Tool Boundary
Implement authorization in APIs, services, databases, gateways or other execution components. Do not rely only on prompts to prevent unauthorized writes.
Step 7: Add Logging and Monitoring
Record access requests, authorization decisions, approvals, executions and failures. Ensure read and write events can be distinguished during review.
Step 8: Test Negative Scenarios
Test whether an agent can access data outside its scope, modify restricted records, exceed transaction limits or execute actions without approval.
Step 9: Review Permissions Regularly
Review permissions when the agent's purpose, connected systems, tools or workflows change. Remove unnecessary access rather than allowing it to accumulate.
Common Read and Write Security Mistakes
Read and write security failures often result from treating system connectivity as unrestricted authority.
- Treating Read Access as Write Authority: Access to retrieve information does not automatically justify permission to modify the same information.
- Relying Only on Prompt Instructions: Prompt instructions can guide agent behavior, but they do not replace technical authorization at the execution boundary.
- Giving Agents Broad API Access: An agent should not receive access to every operation exposed by an API when its task requires only a limited subset.
- Placing Approval After Execution: Approval that occurs after a sensitive change has already been completed does not prevent the original action.
- Ignoring Field Level Controls: Application access may expose sensitive fields that are unnecessary for the agent's task. Data and field level restrictions should be considered where appropriate.
- Failing to Test Unauthorized Requests: Security testing should include attempts to access restricted records, perform prohibited operations, exceed transaction limits and bypass approval requirements.
Read and Write Security Within the Enterprise Intelligence Layer
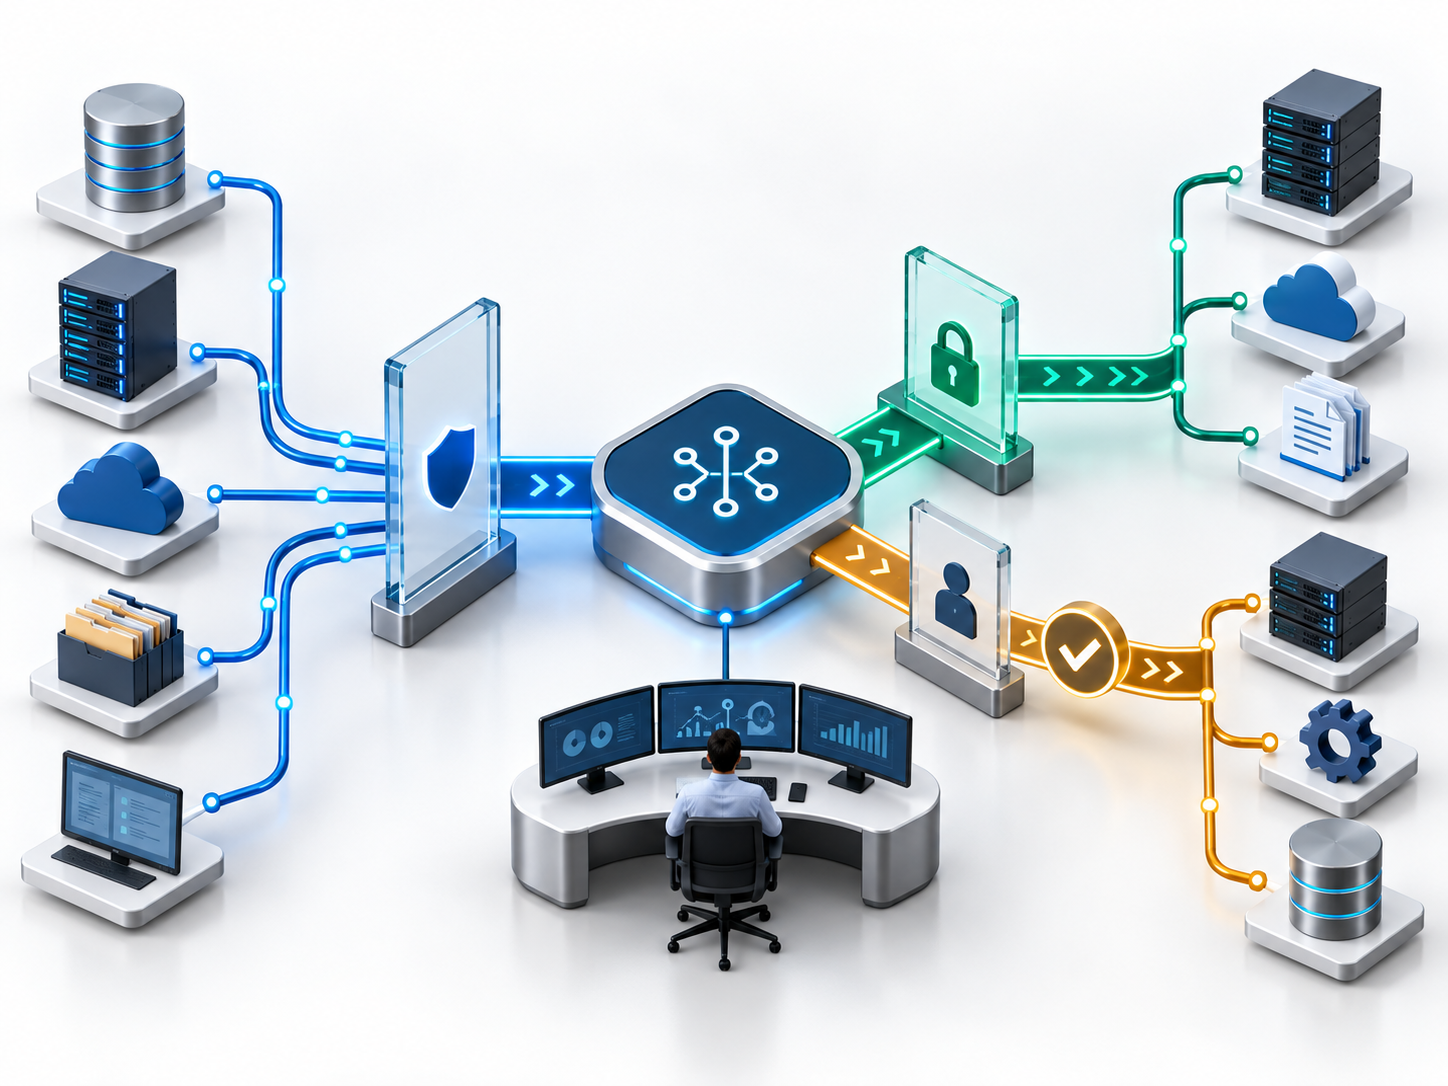
Read and Write Security for AI Agents establishes the technical boundaries within which an Enterprise Intelligence Layer can execute agent based workflows across connected systems.
The intelligence layer can provide shared context, workflow coordination and agent interaction. Read and write security determines which information can be accessed and which actions can be executed within the connected environment.
The relationship can be understood as: Enterprise Context → Agent Request → Access Policy → Operation Authorization → Approval Check → Tool Execution → Audit.
AIQoD's Enterprise Intelligence Layer positioning connects agentic capabilities with enterprise workflow execution across business systems. A security architecture must ensure that intelligence and orchestration capabilities remain subject to defined data access and action authorization controls.
The distinction is important because an agent may identify a recommended action without having authority to execute it. The system must evaluate the requested operation before allowing the change.
Detailed agent ownership and lifecycle governance are covered in the related AI Agent Governance article, while workflow coordination and delegation are covered in the AI Agent Orchestration article.
Conclusion
Read and Write Security for AI Agents helps enterprises separate information access from operational authority. Read permissions, write permissions, tool authorization, transaction limits, approval gates and auditability should be designed together.
A secure agent should receive only the access necessary for its assigned responsibilities. Sensitive or irreversible operations should use stronger authorization and appropriate human oversight.
The objective is not to prevent useful agentic workflows. The objective is to ensure that every important action is bounded, authorized, observable and accountable.
Frequently Asked Questions
What is Read and Write Security for AI Agents?
Read and Write Security for AI Agents separates an agent's permission to retrieve information from its permission to change enterprise data or system state. It helps ensure that access to information does not automatically grant authority to execute sensitive actions.
Why should read and write permissions be separated?
Read access generally retrieves information, while write access can change records, trigger transactions or create operational consequences. Separating them allows enterprises to apply stronger controls to actions that carry greater risk.
How can enterprises prevent unauthorized AI agent writes?
Enterprises can use least privilege, operation specific authorization, field level restrictions, transaction limits, approval gates and enforcement at API or system boundaries. Prompts should not be treated as a replacement for technical access controls.
When should an AI agent require approval before writing data?
Approval is particularly relevant for high impact, sensitive, irreversible, or externally consequential operations. Approval should occur before the action changes the enterprise state.
How should AI agent write operations be audited?
Audit records should capture the agent identity, requested operation, target system, authorization decision, approval status, execution result and relevant context. Records should distinguish proposed actions from completed actions.